Enterprises in regulated industries choose The Apps Developers because we treat compliance as an engineering requirement from day one: we map every rule, like HIPAA or PCI DSS, to a specific technical control, build audit evidence into the deployment pipeline, and deliver the cloud backend, web app, and mobile app with one accountable team. The result is software that can hold up to an audit without slowing the business down.
Talk to anyone who has run a cloud project at a hospital, a lender, or an insurer, and you’ll hear a familiar story. The build went fine. Then the security questionnaire arrived, or the auditor asked who changed a production setting six months ago, and nobody could answer quickly. Weeks of rework followed.
That gap between “it works” and “it passes” is exactly what regulated companies are trying to avoid when they pick a development partner. In this article, we’ll explain how our Cloud App Development team approaches that gap, what makes regulated cloud work different, and the questions you should ask any vendor, including us, before signing.
What Is Cloud Application Development for Regulated Industries?
Cloud application development for regulated industries is the process of designing, building, and running cloud software that meets legal and industry rules for data protection, access control, auditability, and incident response, such as HIPAA, PCI DSS, SOC 2, and GDPR.
The tools are the same ones every cloud team uses: containers, managed databases, APIs, CI/CD. What changes is the proof. In a regulated business, it isn’t enough for data to be secure. You have to show who accessed it, when, why, and what controls stopped everyone else.
Why Regulated Cloud Projects Go Wrong
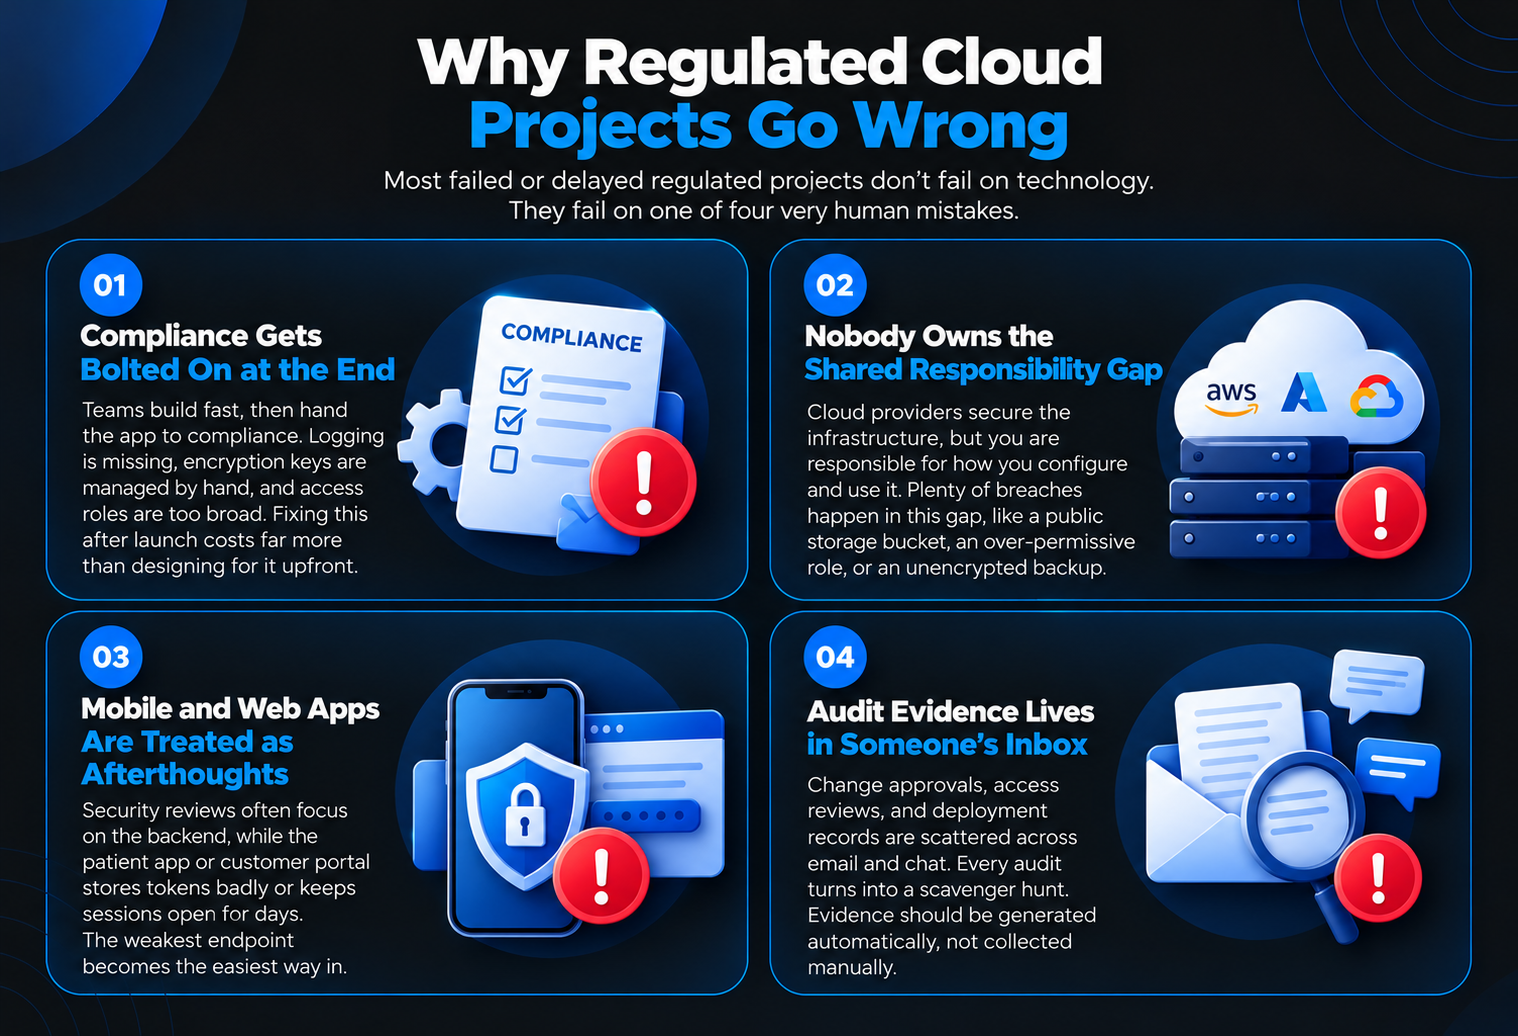
Most failed or delayed regulated projects don’t fail on technology. They fail on one of four very human mistakes.
Compliance Gets Bolted On at the End
A team builds fast, then hands the finished app to the compliance department. Logging is missing, encryption keys are managed by hand, and access roles are too broad. Fixing that after launch costs far more than designing for it upfront.
Nobody Owns the Shared Responsibility Gap
Cloud providers secure the infrastructure, but you are responsible for how you configure and use it. Amazon calls this the shared responsibility model, and Azure and Google Cloud follow the same idea. Plenty of breaches happen in that gap: a public storage bucket, an over-permissive role, an unencrypted backup. The provider did its part. The application team didn’t.
Mobile and Web Apps Are Treated as Afterthoughts
Regulated companies often focus security reviews on the backend, while the patient app or customer portal stores tokens badly or keeps sessions open for days. The weakest endpoint becomes the easiest way in.
Audit Evidence Lives in Someone’s Inbox
When change approvals, access reviews, and deployment records are scattered across email and chat, every audit turns into a scavenger hunt. Evidence should be generated automatically, not collected manually the week before the auditor arrives.
How Regulations Translate Into Cloud Engineering
Regulations rarely tell you which technology to use. They describe outcomes. The real skill is translating those outcomes into specific controls your engineers can build and test. Here’s a simplified version of the mapping we use at the start of every regulated project.dFor healthcare, HHS has published guidance on HIPAA and cloud computing that explains when a cloud provider becomes a business associate and what that means for you.
For payments, the PCI DSS standard sets the technical bar. One of the best ways to reduce your PCI scope is simply to store less card data, which is an architecture decision, not a paperwork one.
7 Reasons Regulated Enterprises Choose The Apps Developers
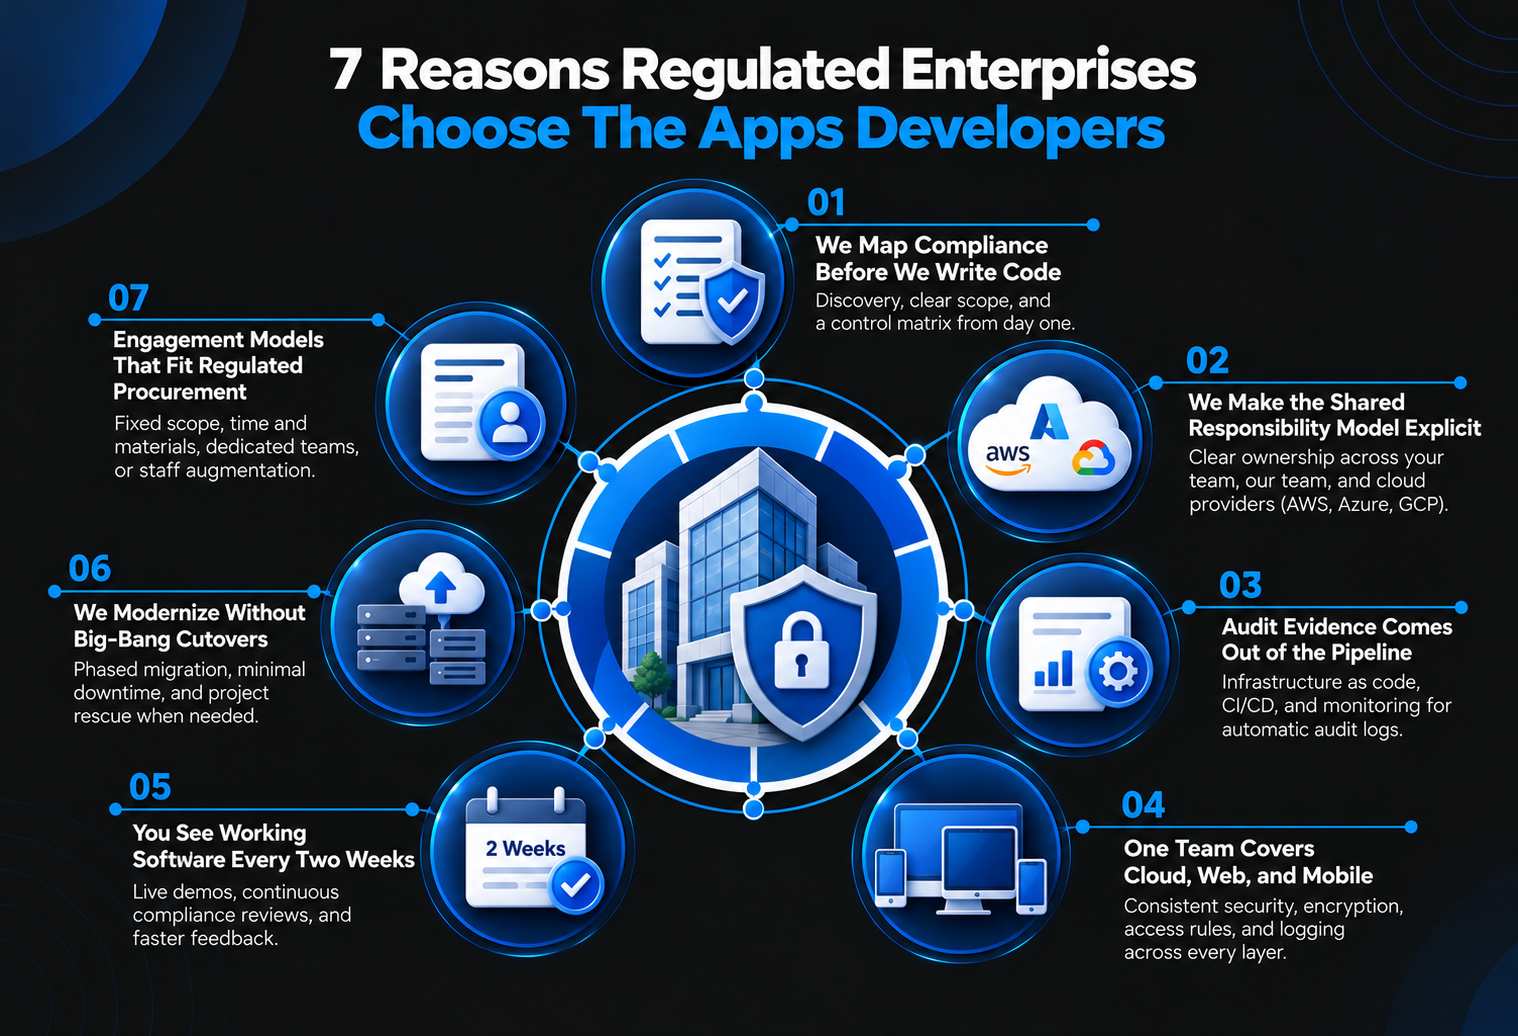
1. We Map Compliance Before We Write Code
Every engagement starts with discovery and a written scope, so both sides agree on what “done” means before development begins. For regulated work, that scope includes a control matrix: each requirement that applies to you, the technical control that satisfies it, and how we’ll test it. Your compliance team reviews it in week one, not month six.
2. We Make the Shared Responsibility Model Explicit
We document exactly which controls the cloud provider covers, which ones our team builds, and which ones your organization owns after handover. We also design around compliance-eligible managed services on AWS, Azure, and Google Cloud, so you inherit as much of the provider’s certified infrastructure as possible instead of rebuilding it yourself.
3. Audit Evidence Comes Out of the Pipeline Automatically
Our DevOps and cloud solutions practice builds infrastructure as code with Terraform, deploys through automated CI/CD pipelines, and monitors with tools like Prometheus, Grafana, and Sentry. That means every infrastructure change is versioned, reviewed, and logged. When an auditor asks who changed a setting and who approved it, the answer is a link, not a meeting.
4. One Team Covers Cloud, Web, and Mobile
Regulated products rarely live in one place. A healthcare platform might have a cloud backend, a clinician web portal, and a patient mobile app. We design, build, and secure all three with the same team, so encryption, access rules, and logging stay consistent across every layer.
That includes the details attackers love, like token storage and session timeouts on shared devices. Our guide to web app session management shows how we handle that layer.
5. You See Working Software Every Two Weeks
We build in two-week sprints with a live demo at the end of each one. For regulated teams, that cadence matters more than it sounds. Your security and compliance reviewers can check controls as they’re built, instead of facing one giant review at the end when changes are expensive.
6. We Modernize Without Big-Bang Cutovers
Many regulated enterprises can’t afford downtime, so we rarely recommend rewriting everything at once. We move legacy systems to the cloud in phases, running old and new side by side and shifting traffic gradually. We also rescue projects that have gone sideways. One fintech founder, Samantha Lowe of AppNova, brought us in on a failing build, and within two sprints our team had diagnosed the architecture problems and laid out a clear rebuild plan.
7. Engagement Models That Fit Regulated Procurement
Some projects need a fixed scope and budget that procurement can approve upfront. Others evolve as requirements become clearer. We offer fixed scope, time and materials, dedicated teams, and staff augmentation, so we can work inside your existing compliance program instead of forcing you into ours.
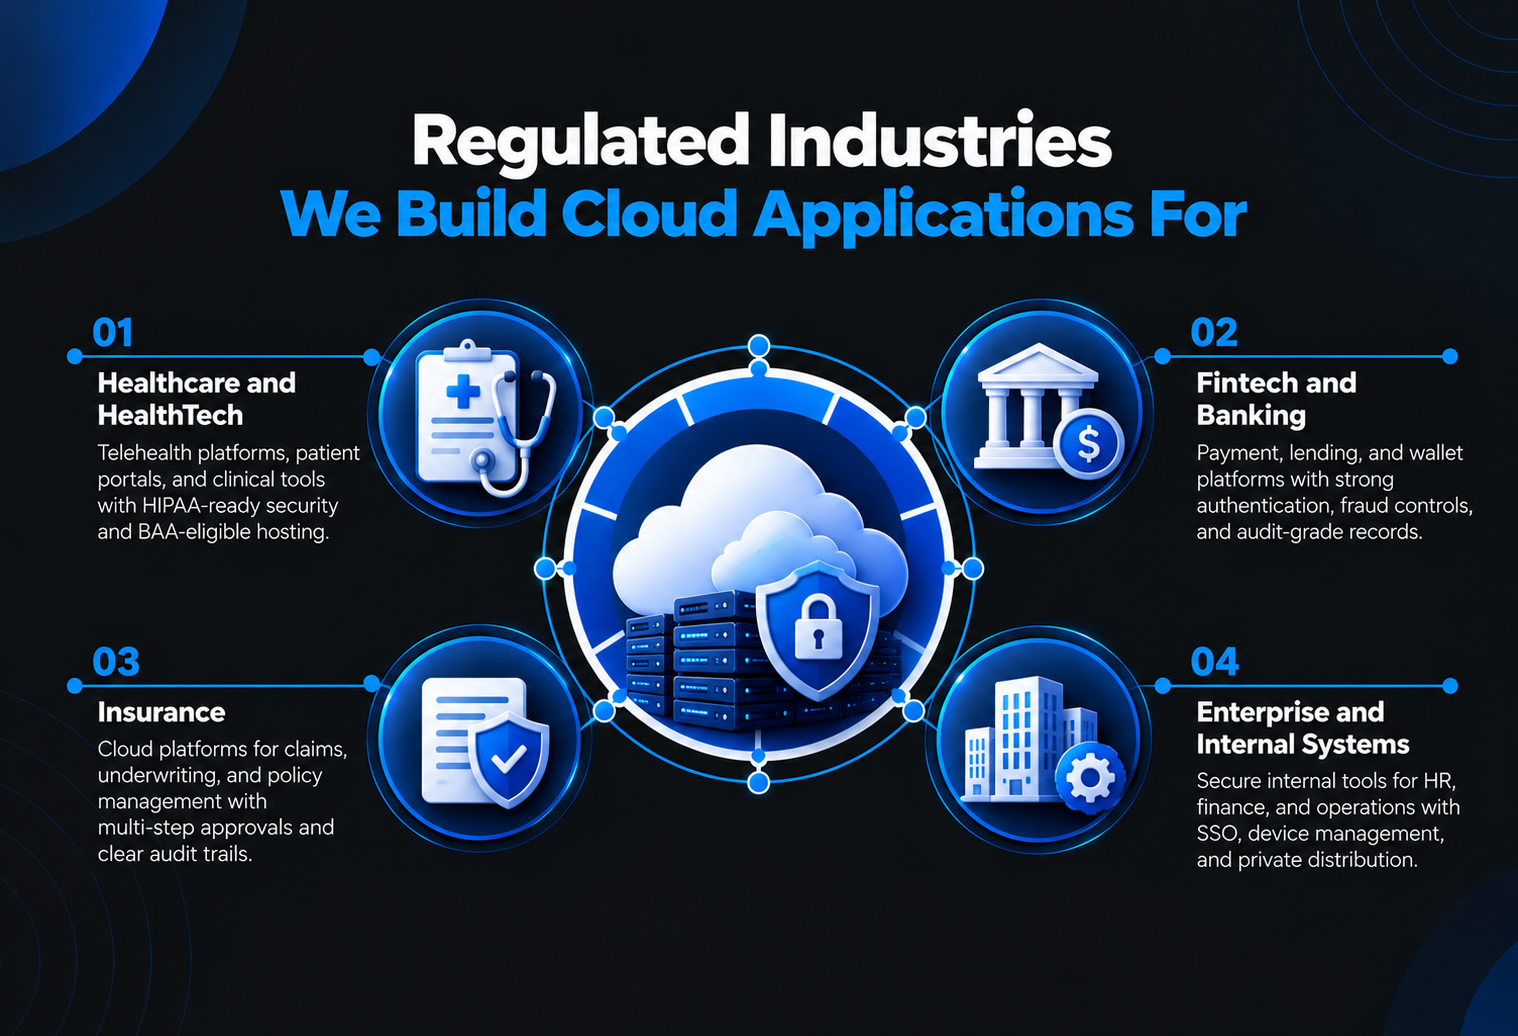
Regulated Industries We Build Cloud Applications For
Healthcare and HealthTech
Healthcare cloud apps have to protect patient data while staying easy enough for tired clinicians and anxious patients to use. Our Healthcare App Development team builds telehealth platforms, patient portals, and clinical tools with encryption, audit logging, and BAA-eligible hosting designed from the start. One HealthTech client, MedLinq, needed HIPAA-conscious architecture ahead of a funding deadline, and our team scoped it in a week and shipped a working MVP in five.
Fintech and Banking
Money apps need audit-grade records for every transaction, strong authentication, and fraud controls built into the flow. Through our Fintech App Development work, we build payment, lending, and wallet platforms that keep cardholder data minimal, tokenize what remains, and log every sensitive action.
Insurance
Insurers deal with claims, underwriting, and policy data that regulators examine closely. We build cloud platforms with multi-step approval workflows, clear audit trails, and role-based access, so every decision on a claim can be traced.
Enterprise and Internal Systems
Not every regulated app faces customers. Internal tools for HR, finance, and operations often hold the most sensitive data of all. For larger organizations, our enterprise mobile app development guide explains how we handle device management, single sign-on, and private distribution.
Architecture Choices That Matter for Compliance
A few early design decisions make compliance dramatically easier or harder later.
Tenant isolation. If you serve many clients from one platform, each client’s data has to stay separate. Our comparison of multi-tenant vs single-tenant SaaS explains when shared infrastructure is fine and when regulated clients need dedicated environments.
Data residency. Some regulations and customers require data to stay in a specific country or region. Choosing cloud regions deliberately at the start avoids painful migrations later.
Software supply chain. Modern apps depend on hundreds of open-source packages, and regulators increasingly expect you to know what’s inside your software. Our guide to open source web application development covers how to choose and track components safely.
Our Process for Regulated Cloud Applications
We follow a security framework rather than inventing one. Our process lines up with the functions in the NIST Cybersecurity Framework, which many regulators and auditors already recognize.
- Discovery and control mapping. We define the scope, identify applicable regulations, and build the control matrix.
- Architecture and threat modeling. We design the system, choose compliance-eligible services, and identify likely attack paths before building.
- Build with guardrails. Infrastructure as code, secure defaults, and automated policy checks keep risky configurations out of production.
- Continuous testing. Automated and manual testing runs throughout the build, including security scans and access control checks.
- Audit-ready deployment. Releases go through automated pipelines with full change records and rollback plans.
- Operate and improve. After launch, we monitor, patch, and evolve the system with a team that already knows your codebase.
Questions to Ask Any Cloud Development Partner
Before hiring any cloud development company for regulated work, ask how they map regulations to controls, who owns each security responsibility, and how they produce audit evidence. Here’s the checklist we’d use if we were in your seat.
| Question to Ask | Why It Matters | What a Good Answer Sounds Like |
| How do you map our regulations to technical controls? | Shows whether compliance is designed in or bolted on | A written control matrix reviewed before development starts |
| Who owns which controls after launch? | Prevents shared responsibility gaps | A documented split between provider, vendor, and your team |
| How is audit evidence produced? | Determines how painful audits will be | Automatically, from CI/CD, infrastructure as code, and logs |
| What third-party audits or attestations do you hold? | Helps your procurement team assess vendor risk | A clear, honest list with scope, plus how they work within your own compliance program |
| How do you secure mobile and web clients? | Endpoints are a common breach point | Specific answers on token storage, session timeouts, and encryption |
| How will you modernize without downtime? | Regulated services can’t go offline | A phased migration plan with rollback options |
A good partner welcomes these questions. If a vendor gets vague on any of them, that tells you something too.
Conclusion
Regulated enterprises don’t need a partner who just knows the cloud. They need one who understands that every architecture decision eventually has to be explained to an auditor. That’s why companies in healthcare, fintech, insurance, and enterprise operations choose The Apps Developers: compliance mapped before code, evidence built into the pipeline, and one team accountable for the backend, web, and mobile experience.
Planning a cloud application in a regulated industry? Book a free consultation with The Apps Developers, and we’ll walk through your regulations, your current architecture, and a realistic plan to build or modernize with confidence.
Frequently Asked Questions
What is cloud application development for regulated industries?
It’s building and running cloud software that meets rules like HIPAA, PCI DSS, SOC 2, and GDPR. That means designing encryption, access control, audit logging, and incident response into the app from the start.
Is AWS, Azure, or Google Cloud HIPAA compliant?
No cloud is compliant on its own. AWS, Azure, and Google Cloud offer HIPAA-eligible services and sign business associate agreements, but you’re still responsible for configuring and using those services correctly.
Who is responsible for security and compliance in the cloud?
Responsibility is shared. The cloud provider secures the underlying infrastructure, while the application owner and development partner are responsible for configuration, access, data protection, and how the app is built.
Can legacy systems move to the cloud without downtime?
Usually, yes. A phased migration runs the old and new systems side by side and moves traffic gradually, which lets regulated services stay online throughout the transition.
How long does it take to build a compliant cloud application?
It depends on scope and integrations. A focused MVP can launch in a few months, while enterprise platforms with legacy migrations and many integrations often take six months to a year or more.
What should I ask a cloud development partner before hiring them?
Ask how they map regulations to controls, how they split security responsibilities, how they generate audit evidence, what attestations they hold, and how they secure web and mobile clients.